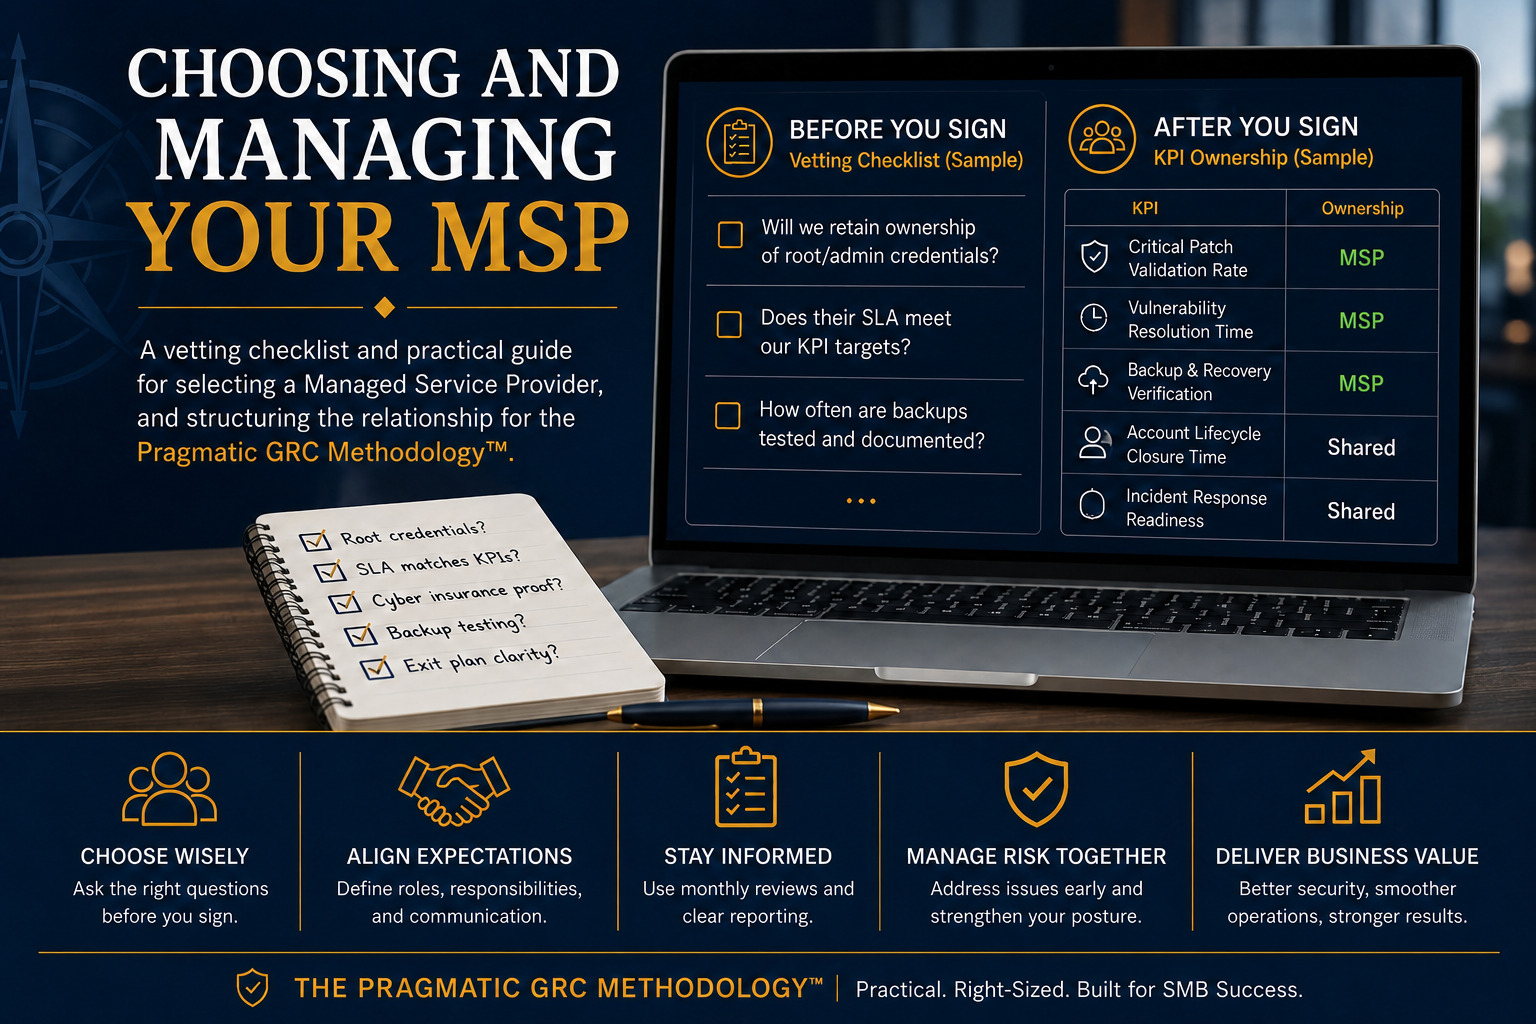
Why This Deserves Its Own Page
If you’ve read this far in the book, you’ve already met your MSP more than once—whether you noticed it or not. The very first case study in Chapter 1, “The Vanishing Managed Service Provider,” is an MSP relationship gone wrong. Chapter 4 warns you explicitly about who holds your root administrative credentials. By Chapter 6, “IT Manager or MSP” is listed as the owner for most of your five KPIs.
In other words: the methodology assumes you have one, trusts it with real authority, and never once tells you how to choose it well or manage it once it’s in place. This page closes that gap.
What Good and Bad Actually Look Like
Before the checklist, it helps to know what you’re watching for. Most MSP relationships don’t fail all at once—they drift, one skipped update or one vague answer at a time.
Signs You’re in Good Hands
- They can tell you exactly who holds your root/admin credentials, and it’s a name you recognize on your own team, not just theirs
- They send you monthly reports without you having to ask
- They welcome an independent security review instead of resisting it
- They tell you about a mistake before you find it yourself
Signs Worth a Hard Conversation
- Only they know the admin passwords, and getting them requires a support ticket
- Patch and backup reports are vague (“all good”) rather than specific
- They get defensive when you ask for evidence, not just a status update
- Offboarding a departed employee takes days, not minutes
Before You Sign: The Selection Checklist
Use this during the vetting conversation itself, not after you’ve already decided. Every question here maps to something this methodology actually depends on later.
MSP Selection Checklist
Ten questions worth a straight answer before you sign anything.
After You Sign: Structuring the Relationship
A good MSP contract doesn’t end the work—it just tells you what the MSP is actually responsible for once the Pragmatic GRC Methodology™ is running. Most SMBs split ownership of the five KPIs between internal staff and their MSP roughly like this:
| KPI | Typically Owned By |
|---|---|
| Account Lifecycle Closure Time | Shared — HR initiates, MSP executes |
| Critical Patch Validation Rate | MSP |
| Vulnerability Resolution Time | MSP, with business owner sign-off |
| Backup & Recovery Verification | MSP |
| Incident Response Readiness | Shared — business owner leads, MSP supports |
Put this ownership split in writing, even informally, before your first Monthly Heartbeat. The single most common breakdown isn’t a technical failure—it’s both sides assuming the other one was watching a metric that neither one actually was.
Want Help With This Conversation?
Vetting or resetting an MSP relationship is exactly the kind of conversation that benefits from someone who’s sat through it before—on both sides of a good outcome and a bad one.
Bring This Checklist to Your Next MSP Conversation
Whether you’re choosing a new provider or resetting expectations with your current one, this is exactly the kind of engagement the Pragmatic GRC Methodology™ was built to support.
Get the Book → Talk to an Advisor →