The Pragmatic GRC Methodology™
Governance Doesn’t Have to Be Complicated.
Practical Governance, Risk, and Compliance for Small and Medium-Sized Businesses.
Most Governance, Risk, and Compliance (GRC) frameworks were designed for large enterprises with dedicated compliance departments and extensive resources. Small and medium-sized businesses often face the same business risks but without the staff, budget, or time to manage complex governance programs.
The Pragmatic GRC Methodology™ was created to change that. It simplifies GRC into a practical operating system that helps organizations identify their critical assets, understand business risks, strengthen cybersecurity, and build sustainable governance practices — without unnecessary bureaucracy.
Whether you’re just getting started or looking to improve an existing program, you’ll find practical guidance, downloadable templates, and real-world examples designed specifically for SMBs.
A 30-Second Gut Check — From Chapter 1
Three Questions Every Business Leader Should Be Able to Answer
If you can answer these with confidence, you’re already thinking like a governance leader.
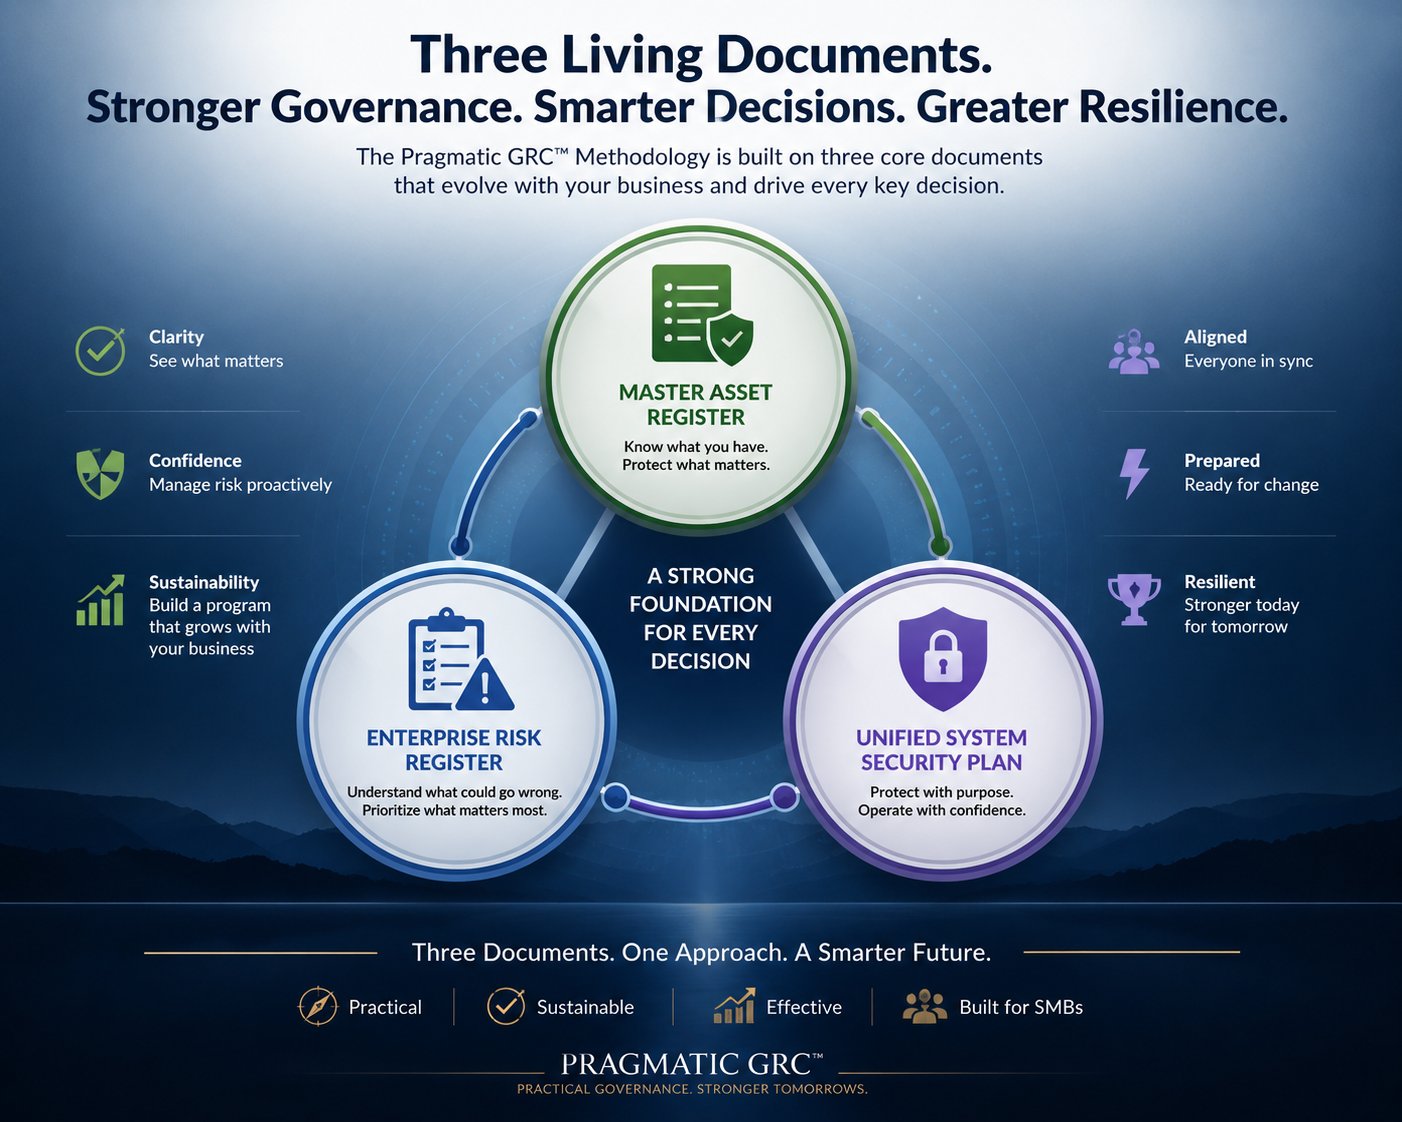
Start with the Three Living Documents
Everything in the Pragmatic GRC Methodology™ revolves around three core documents that evolve alongside your business — a Master Asset Register, an Enterprise Risk Register, and a Unified System Security Plan.
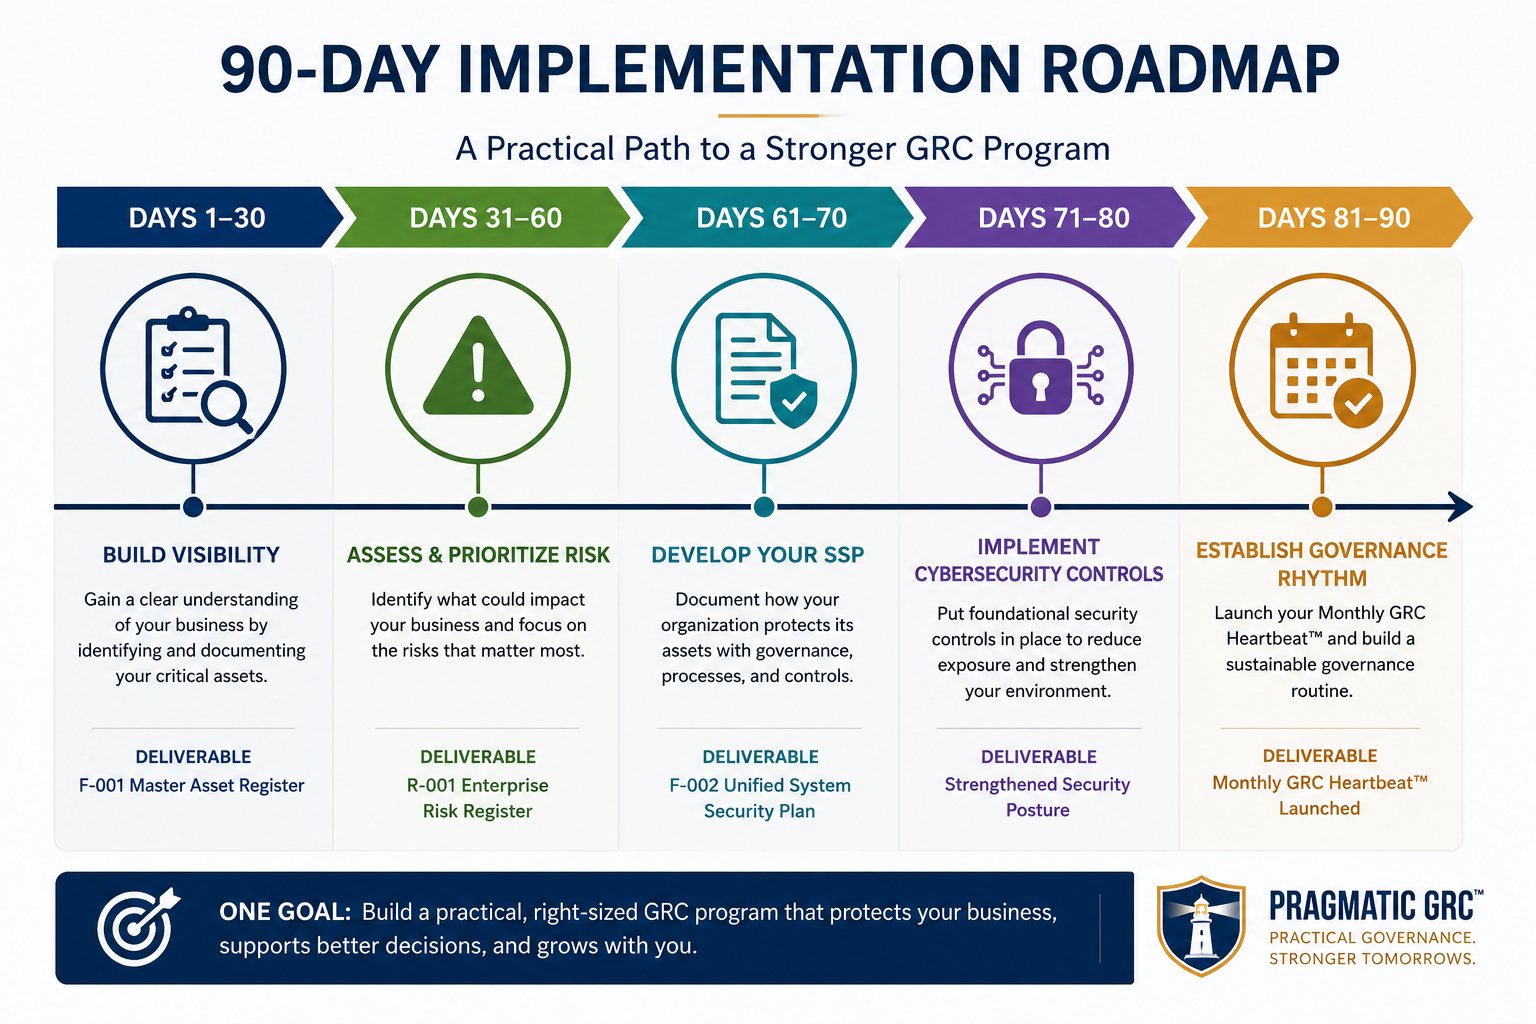
Implement in 90 Days
Getting started doesn't require months of planning. Our practical roadmap builds a right-sized GRC program in five manageable phases.
Explore the Resource Center
The companion Resource Center extends the book with practical tools you can use immediately.
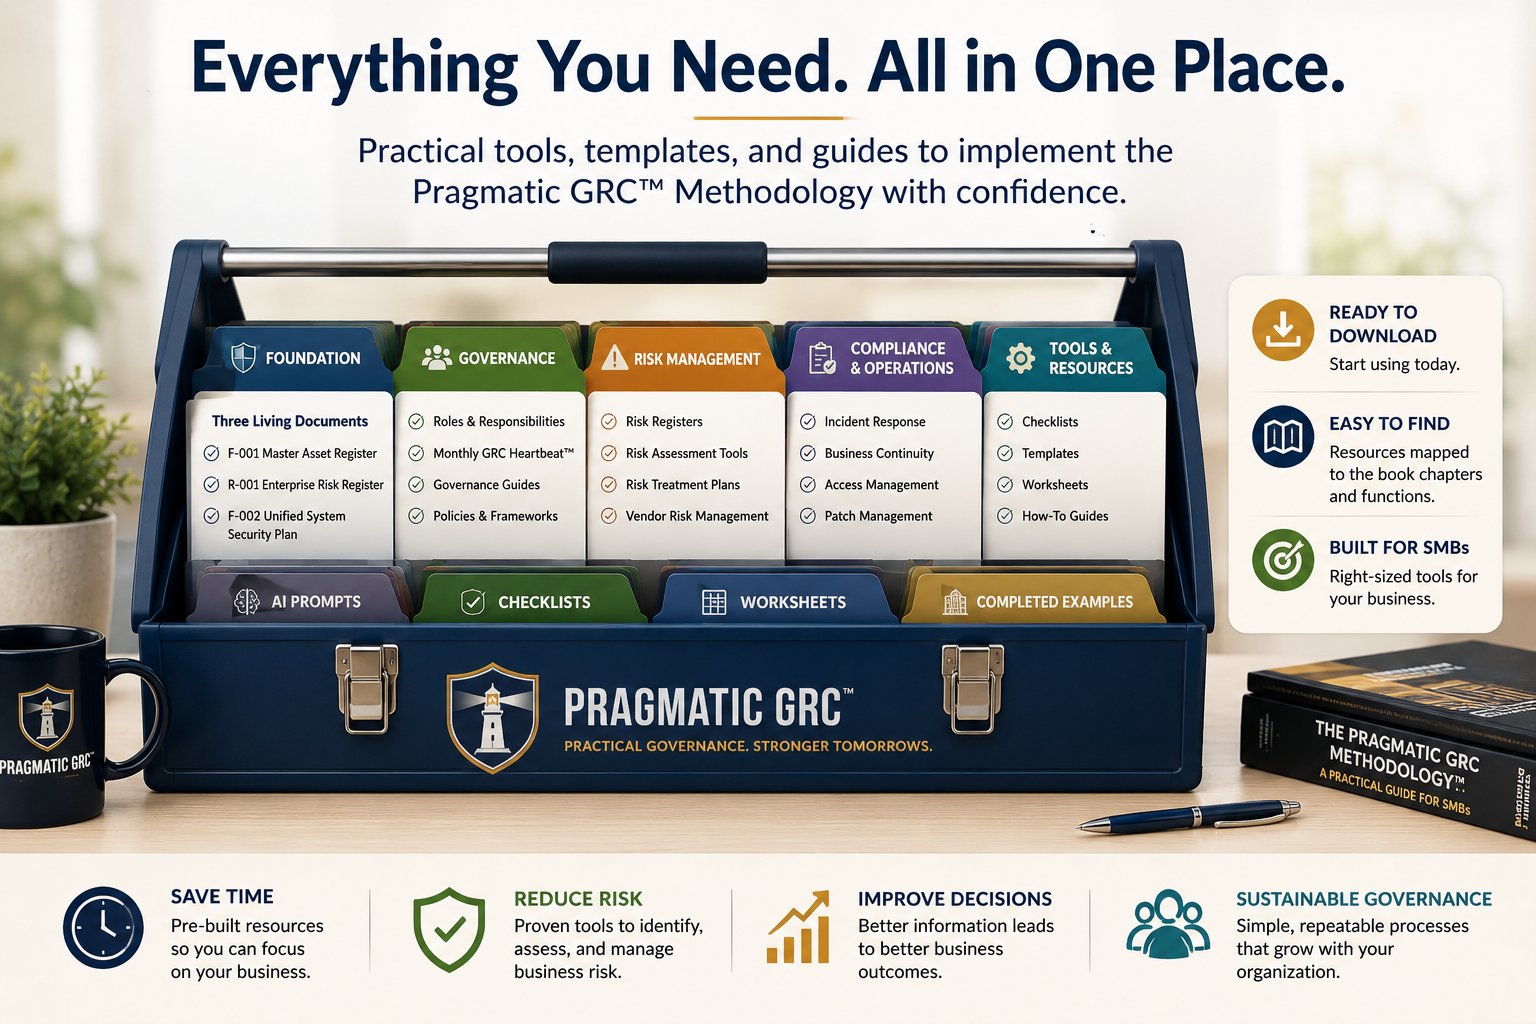
Available resources include:
- Downloadable templates
- Implementation guides
- Checklists
- Completed examples
- AI prompts
- Governance worksheets
- Reference documents
Each resource is mapped to the relevant chapter in the book, making it easy to find exactly what you need.
See the Methodology in Practice
Wondering what a completed GRC program looks like?
OFMA Healthcare Reference Implementation
Explore Orrville Family Medical Associates (OFMA), a fictional small medical practice that demonstrates how the Pragmatic GRC Methodology™ can be applied in a real-world business environment. See completed examples of the Three Living Documents and how they work together to support governance, risk management, and cybersecurity.
See the Example →About the Book
The Pragmatic GRC Methodology provides a practical roadmap for building a governance, risk, and compliance program without the complexity of enterprise frameworks.
Through straightforward explanations, real-world examples, implementation guidance, and companion resources, the book helps organizations transform GRC from an annual compliance exercise into an ongoing business capability.
Ready to Get Started?
Whether you're reading the book, downloading templates, or exploring the completed examples, you're taking the first step toward building a more resilient organization.